What is an Annual Review? What your Annual Compliance Review Should Cover
By: Meghan Sundquist, Compliance Consultant
What Your Annual Compliance Review Should Cover
Background
In 2003, the SEC adopted Rule 206(4)-7 of the Investment Advisers Act establishing three core compliance requirements for investment advisers registered or required to be registered under section 203 of the Act in order to legally provide investment advice to clients:
“Adopt and implement written policies and procedures reasonably designed to prevent violation, by you and your supervised persons, of the Act and the rules that the Commission has adopted under the Act;
Review, no less frequently than annually, the adequacy of the policies and procedures established pursuant to this section and the effectiveness of their implementation; and
Designate an individual (who is a supervised person) responsible for administering the policies and procedures that you adopt under paragraph (a) of this section.”
If you’re new to the industry, a newly registered investment adviser, or a new compliance professional, this may be new to you. If you’ve been around the block, you are most likely familiar with this rule.
In our last blog post, we discussed requirements for new advisers registering with SEC. If that’s you, or if you’re new to the world of SEC compliance, we wanted to provide some more information on the annual compliance review. If you’re here looking for another perspective, we hope this will be helpful as well.
This article will tackle requirements (a) and (b) above with the emphasis being on designing a robust annual review process that shapes your compliance program. There’s a lot of ground to cover, so let’s dive in.
Every advisory firm is different, and there is no single annual review checklist that applies to every firm. The topics and questions below are not intended to be exhaustive. Instead, they are designed to help you identify areas that may warrant review based on your firm’s business model, risks, conflicts, and regulatory obligations.
Do You Know Your Firm’s Actual Practices?
Before discussing how to design an annual review, it is important to understand what the rule actually requires: an assessment of the adequacy of the firm’s policies and procedures and the effectiveness of their implementation. The annual review should not simply confirm that a policy exists. It should consider whether the policy reflects what the firm actually does and whether the controls designed to support that policy are working.
There are many different templates out there, but the key here is to ensure they are tailored to your firm’s actual practices. If your firm does not have any soft dollar arrangements, you probably don’t need a soft dollar policy. To start developing your firm’s policies and procedures, start by taking inventory of the firm’s practices and figuring out which rules apply to you.
Understand Your Business and Regulatory Obligations
Start by taking inventory of the firm’s business practices and determining which rules and regulatory requirements apply.
Are you an investment adviser? Are you a private fund or private fund adviser? Are you a broker dealer? Are you a combination of different types of entities?
Based on your answers to the above, which regulatory filings are you obligated to complete? We put together a compliance calendar of regulatory filings for 2026. You can view that here. Some common ones are:
Form ADV
Form 13F
Form N-PX
Form D
Form PF
State Notice filings
U4
Does the firm manage ERISA plans or recommend DOL rollovers? If so, be sure the firm has appropriate bonding, disclosures, and documentation in place.
Depending on your firm’s size, trading volume, and types of assets, are there other regulation requirements that apply?
Do you know the various state requirements and whether employees are required to be registered as an IAR? Does your state require IAR CE? Are your reps required to complete any other type of CE (insurance, BD)?
Review Employee Oversight and Conflicts of Interest
Next, consider how the firm supervises its employees and identifies and manages conflicts of interest.
Are you aware of any disciplinary events, old or recent? Are there any outside business activities? How would you substantiate your answers to these questions to the SEC (attestations, etc.)?
To read more about various Code of Ethics requirements, read the Code of Ethics rule here.
If your Code of Ethics has a gifts/entertainment policy and/or political contributions policy, ensure they reflect your firm’s practice and meet SEC requirements.
Are your employees engaged in outside business activities?
How are you staying aware of conflicts of interest (trading, solicitor arrangements, financial arrangements etc.)?
Are you aware of what your employees are using and communicating through electronic communications? A lot can happen in an email thread or text message. How often do you review these? Are they archived and retrievable? How would you substantiate this to the SEC?
Who reviews the firm’s financials? Are you aware of the incoming fees the firm is earning and the expenses being paid for consistency in disclosures and policies?
How do you ensure your employees are aware of the firm’s policies and procedures and SEC regulations?
How would you prove to the SEC that your firm values and supports compliance?
Do you conduct due diligence on any service providers you engage? How often? Is it documented?
Review Client Protection and Advisory Practices
After reviewing employee oversight and conflicts, consider the processes and controls that directly affect clients. This can include client onboarding, trading, billing, contracts, disclosures, suitability, and other advisory activities.
What is your client onboarding process? Are contacts consistent? Are required disclosures delivered timely? Who is responsible for an OFAC check and KYC requirements?
How are client trades managed? Are they reviewed regularly for signs of unusual patterns, best execution, portfolio pumping, insider trading, and trade errors? Does the firm have a trade error log? Are there any specific valuation procedures that are not documented?
Does the firm have any guidelines/suitability review? Do clients receive reports? Are they reviewed?
Does the firm have custody? This is a complicated one, so we would recommend doing some research into the various ways a firm can end up with custody and whether a surprise exam is needed. See the Custody Rule here. We also have two blog posts on this topic – click here for part 1.
Does the firm vote proxies? Is this disclosed in the firm’s ADV and client contracts? And if using a third party do you have the proper oversight procedures of the provider?
Is the firm’s billing process documented in such a way that someone could duplicate the process by just reading the manual? Is it disclosed to clients in the ADV? Are there any exceptions? How often is billing reviewed?
How are client complaints handled? Are they documented along with resolutions? Does your staff know what a compliant is and how to report it for a timely response?
Does the firm ever engage in agency cross transactions?
You can read the rule here.
Does the firm have senior investors? Is staff trained to recognize signs of diminished capacity or elder abuse and the firm’s course of action if these are present?
Review Firmwide Operational Risks and Controls
Finally, consider the broader operational risks that can affect both clients and the firm.
Does your firm have a business continuity plan? Is it updated and do employees have a copy?
Is the firm retaining the appropriate records? Click here to read the Books and Records rule.
How is your firm’s cybersecurity? Is this reviewed with IT periodically? What protocols are in place to ensure protection of client information? Be sure to read Regulation S-P and amendments in addition to any rules the SEC has released on cybersecurity and incident disclosure requirements.
Does the firm utilize Artificial Intelligence/LLMs in any capacity? What about the firm’s vendors?
Is the firm retaining required books and records, and are those records readily retrievable?
These questions are intended to help you identify the areas of your compliance program that warrant further review. The specific areas you test, how frequently you test them, and the depth of that testing should reflect your firm’s business activities, conflicts, regulatory requirements, and risk profile.
Document and Document Some More
As you work through these questions, the various rules and regulations, and filings, be sure to document which apply to your firm and what level of risk they present. How likely are they to happen? If an incident did occur, how would it impact your firm? Consider the likelihood and potential impact of each identified risk and whether the firm’s existing controls appropriately address it. As you work through this list and the various risks and conflicts, you can use this information to provide structure to your annual review.
Create a Compliance Calendar
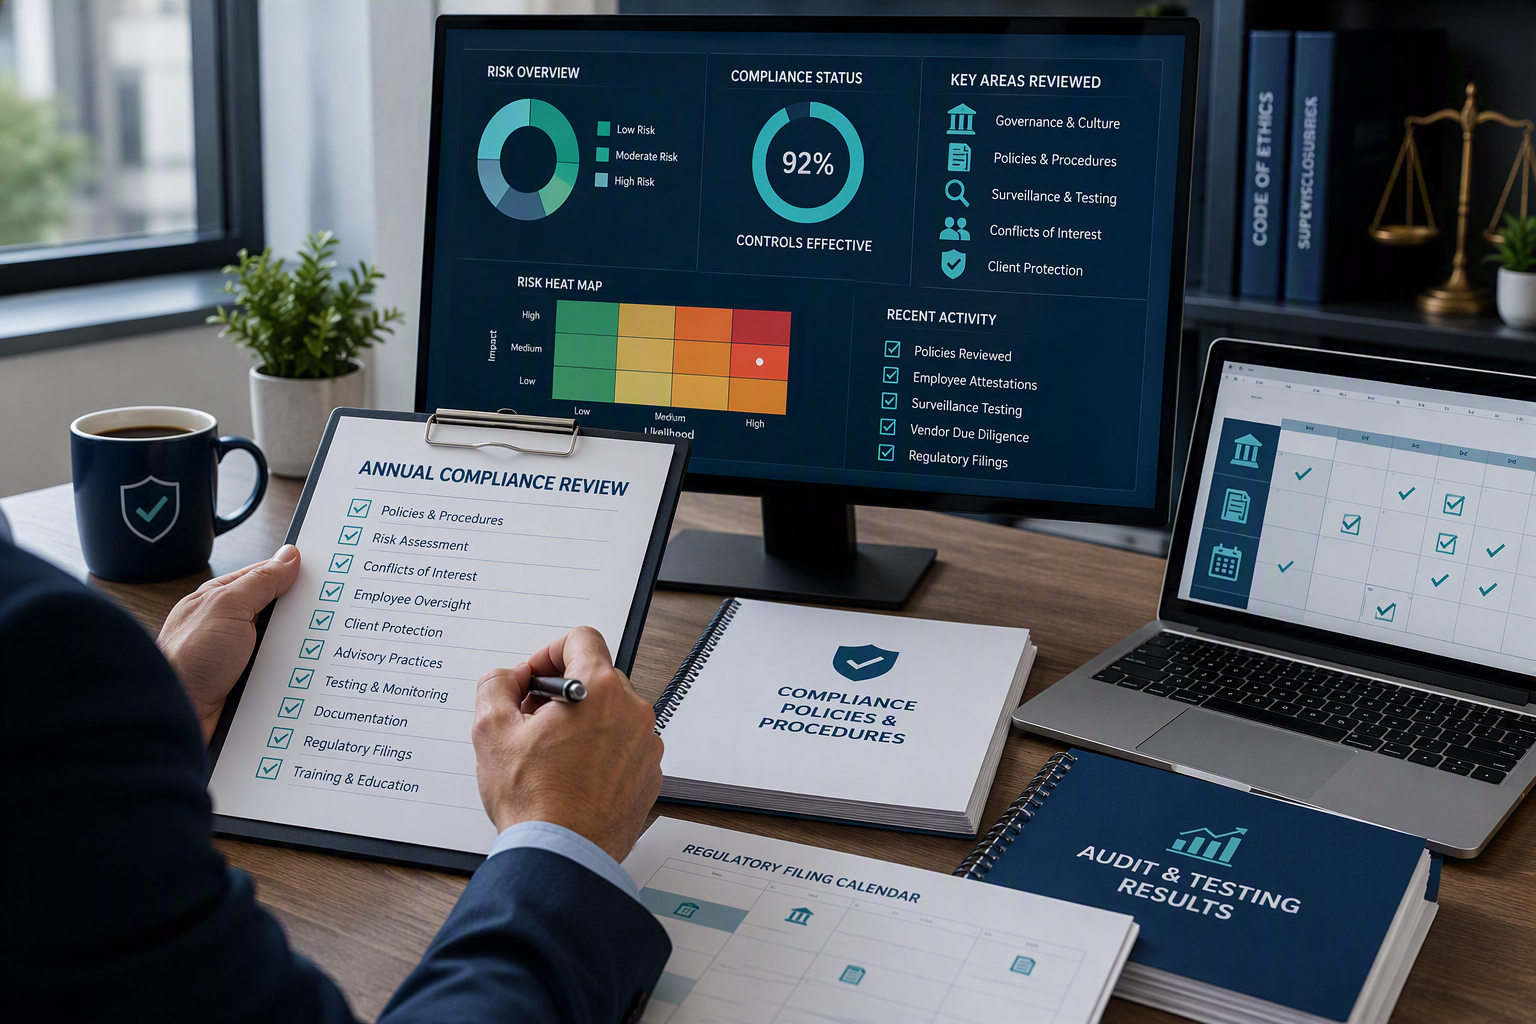
An annual review does not have to be performed all at once. In fact, for many firms, the most effective approach is to conduct testing throughout the year and use a compliance calendar to make sure higher-risk areas, regulatory filings, and recurring reviews are completed on schedule.
Once you’ve put together your list of risks based on your firm’s processes, you can put together a compliance calendar to provide structure to your annual review.
Note the dates applicable filings are due.
Decide what items are higher risk for your firm and do periodic testing/review of those throughout the year. Decide when you will complete this and add it to the calendar so it does not get missed.
Identify who is responsible for providing and reviewing the various items you will test throughout the year.
Ensure this calendar is shared with all applicable parties.
This will create the structure of your annual review. As you review, test, and edit throughout the year, be sure to save these items in a central location or ease of retrieval. This includes tested documents, redlined and finalized drafts, and any memos. Once all items have been completed, create a memo documenting everything reviewed, updated, and submitted to summarize the annual review. At the conclusion of the review period, prepare the appropriate documentation summarizing the areas reviewed, testing performed, findings identified, and any resulting changes to the compliance program. Supporting documentation should be retained in an organized and readily retrievable manner.
Conclusion
The annual review process can feel overwhelming, particularly for a new CCO or a growing advisory firm. The questions in this article are not intended to cover every area that may apply to your firm. Instead, we hope they provide a practical starting point for identifying your firm’s risks, evaluating whether your policies and procedures reflect actual practices, and developing a review process that evolves with your business.
As always, SCS is here to help with any part of your annual review process through our CCO Companion service. If you have any questions, feel free to reach out here to meet with one of our lead consultants.